Numerous vulnerabilities are detected every day. That’s a good thing and a key benefit of using open source products. At m6web we don’t want to be exposed to known vulnerabilities, so we use a service provided by Sensiolabs in our continuous integration tool (Jenkins) to check it.
Just add those lines in your ant build file (and adapt basedir) :
    <!-- =================================================================== -->
    <!-- Security checker                                                    -->
    <!-- =================================================================== -->
    <target name="sf2-security-checker">
     <exec executable="bash" dir="${basedir}/sources/bin" failonerror="true">
         <arg value="-c"/>
         <arg value="curl -Os https://get.sensiolabs.org/security-checker.phar" />
     </exec>
     <exec executable="php" dir="${basedir}/sources" failonerror="true">
         <arg line="${basedir}/sources/bin/security-checker.phar security:check composer.lock" />
     </exec>
    </target>
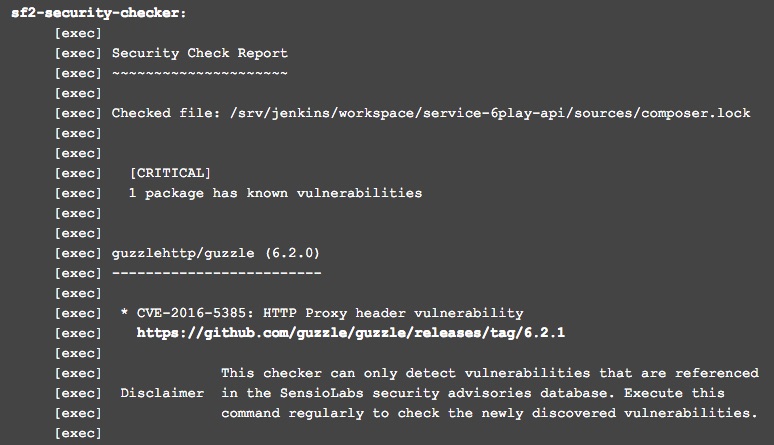
And automatically check your composer.lock againts vulnerabilities. Your build will fail if something wrong is detected.
For example, with the recent Guzzle one :
You can contribute to the vulnerabilities database and the checker via Github.com.